Windows & network troubleshooting · By Ali · Source checked 21 October 2026
A connection that suddenly asks for credentials can look like a Wi-Fi or VPN fault. Before rebuilding the profile, check whether Windows is blocking a legacy Single Sign-On authentication flow.
Microsoft’s October 13 security updates change the default handling of NTLMv1-derived Single Sign-On credentials on affected systems. Some MS-CHAPv2 connections may stop connecting automatically.
Scope: This is an explanation of Microsoft’s published guidance, with a suggested triage workflow. It is not a reproduced lab result or a fix for every Wi-Fi or VPN failure.
Microsoft’s guidance explains the NTLMv1-derived authentication changes that can affect automatic Wi-Fi, Ethernet and VPN sign-in on affected devices.
1. Check whether this change applies
Microsoft identifies Windows 11 24H2 and later listed releases, plus Windows Server 2025. The new default applies when Credential Guard is disabled and BlockNtlmv1SSO is absent. Certain Wi-Fi, Ethernet and VPN connections using MS-CHAPv2-based SSO can be affected. Devices with Credential Guard enabled already restrict this behavior.
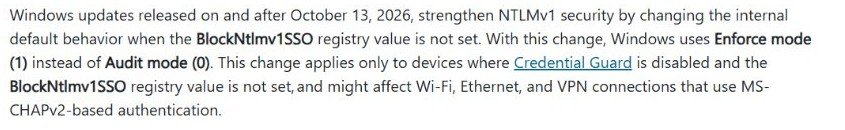
Microsoft says manual credential entry continues to work in Enforce mode. That distinction is useful: record whether automatic sign-in fails while a manual sign-in succeeds.
2. Start with evidence, not a workaround
- Record the symptom. Does the network appear? Is there a credential prompt? Does the failure happen before or after authentication?
- Record the Windows version and installed update. Use
winverand Settings → Windows Update → Update history. Timing alone does not establish the cause. - Ask the network administrator about the authentication method. Separate an MS-CHAPv2 SSO dependency from certificate-based authentication or a different VPN sign-in method.
- Correlate the logs. Match client events with the connection attempt and the corresponding network authentication logs. Redact identities and server names before sharing evidence.
Record time, Windows build and update
MS-CHAPv2 SSO · Credential Guard off · registry value absent
If the evidence does not match, investigate other causes
Review certificate-based authentication
3. Find the relevant event
In Event Viewer, open Applications and Services Logs → Microsoft → Windows → NTLM → Operational. Microsoft documents 4025 for a blocked request in Enforce mode and 4024 for an audited request.
This read-only PowerShell example looks for those events from the past seven days:
Get-WinEvent -FilterHashtable @{
    LogName = 'Microsoft-Windows-NTLM/Operational'
    Id = 4024, 4025
    StartTime = (Get-Date).AddDays(-7)
} | Select-Object TimeCreated, Id, Message
No results do not rule out other authentication issues. The log may also be unavailable or require appropriate access. This example has not been validated against an affected lab in this article.
4. Choose a durable remediation
Microsoft recommends moving MS-CHAPv2 connections toward certificate-based authentication, such as EAP-TLS or PEAP-TLS. Its guidance also describes a temporary Audit-mode exception, which reduces protection.
For a support handoff, include the failure time, build, authentication method and matching event. Agree on ownership and a test plan before changing an enterprise authentication policy.
Question for the community: Which evidence helped your team distinguish an authentication change from a general connectivity problem? Share a sanitized lesson, without internal logs or credentials.
- Microsoft Support — KB5066470: Manage NTLMv1 changes and prevent network authentication issues in Windows (updated 19 October 2026).
- Microsoft Learn — Credential Guard considerations and known issues.
Explanation and diagram by Ali. Technical behavior attributed to Microsoft. Source checked 21 October 2026.